
Dependabot inactive repositories need a monitoring review before you interpret an empty alert view. No visible finding can mean several things: no detected issue, missing dependency coverage, disabled monitoring or archived alerts. Those possibilities do not support the same conclusion.
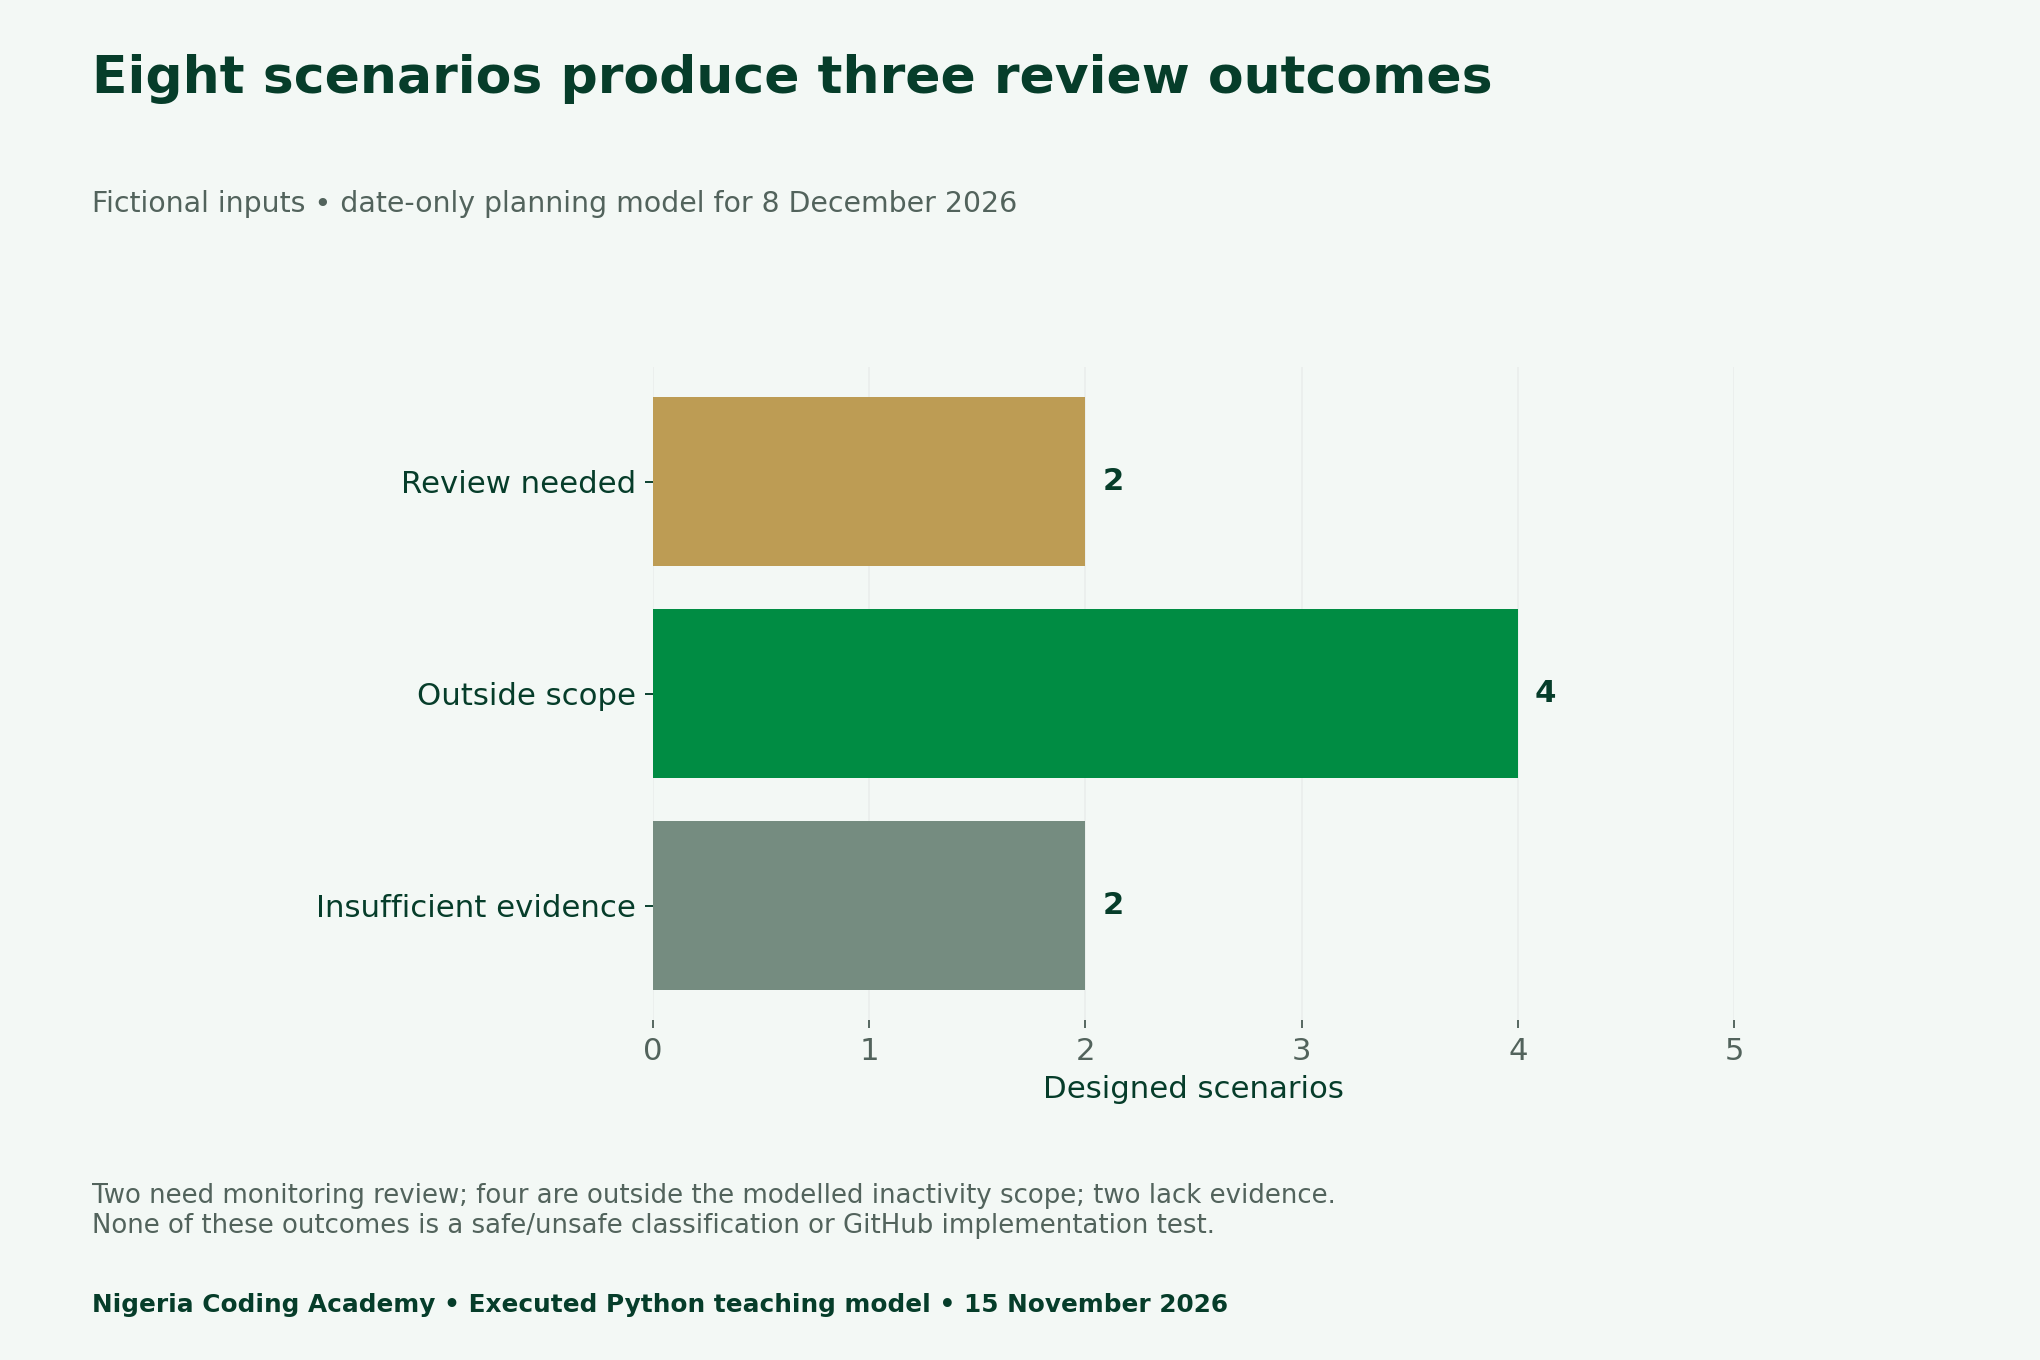
We tested eight fictional portfolio-repository scenarios with a local Python review model. Two need review, four fall outside its inactivity scope and two retain insufficient evidence. The exercise changes no GitHub settings and makes no claim about how many Nigerian repositories will be affected.
The announced change for Dependabot inactive repositories
GitHub’s 10 November notice says that from 8 December 2026, GitHub will disable alerts on most repositories inactive for a year. GitHub archives existing alerts rather than deleting them. Qualifying activity includes a push to any branch or tag, repository creation, or enabling alerts. A push or manual re-enablement restores archived alerts and restarts the clock.
The announcement excludes repositories covered by enforced configurations enabling alerts and specified enterprise policies restricting alert-setting changes. It covers GitHub.com and Enterprise Cloud with data residency, not Enterprise Server. This is a scheduled rule, not a claim that every older repository is already paused on our 15 November research date.
Why no alert is not a security certificate
An alert view is an interface observation. To interpret it, first establish whether monitoring is operating. Next, determine whether the relevant dependencies are represented. Finally, inspect how the maintainer reviewed actual findings. A blank view answers none of those questions on its own.
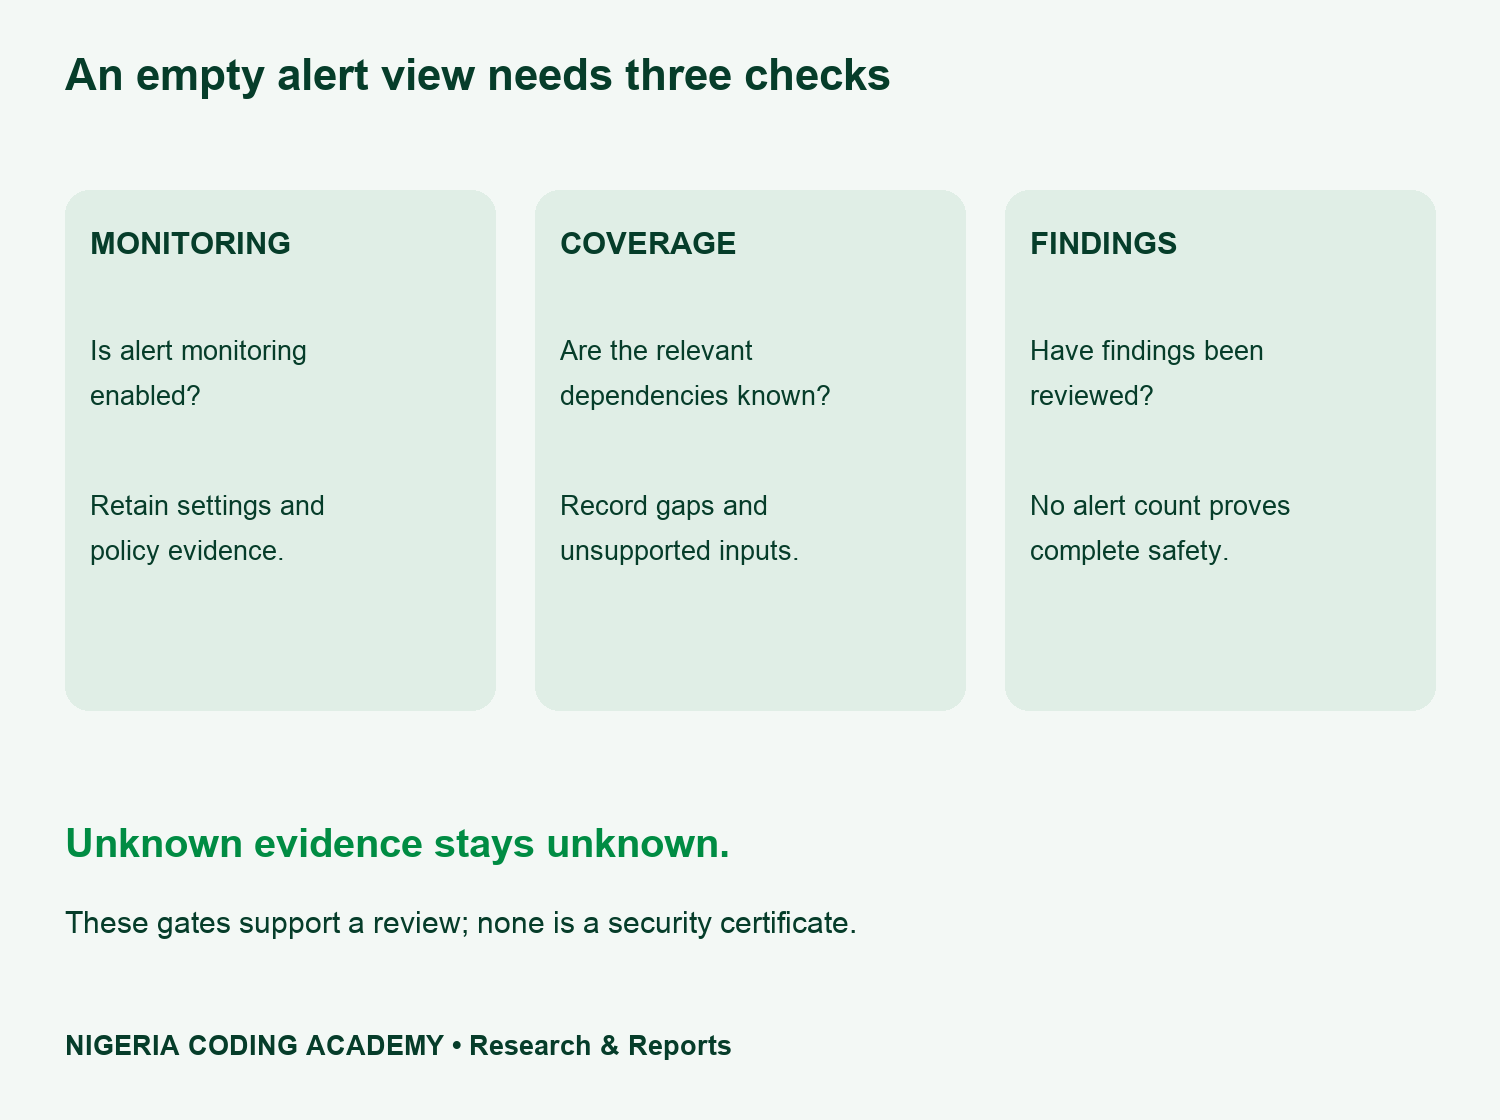
A portfolio README can state the date and scope of a dependency review. It should not turn “zero visible alerts” into “the project is secure.” Moreover, a codebase can contain issues beyond the scanner’s coverage, and restoring monitoring does not repair a vulnerable dependency.
The eight fictional scenarios
Our inputs describe an old push, recent issue discussion without a qualifying event, a recent tag push, a newly created repository, recently enabled alerts and a known enforced-configuration exception. Two further cases deliberately withhold evidence or sit exactly on a calendar anniversary.
The recent discussion case is useful because ordinary conversation is not one of the three qualifying events listed in the notice. However, the exercise does not query real activity streams. We invented each date and policy flag and retain them explicitly in the scenario CSV.
The date-only model keeps a boundary unresolved
We use 8 December 2026 as a planning date and compare the fictional qualifying dates with 8 December 2025. Dates clearly before or after that boundary produce a review outcome when policy evidence is sufficient. However, the exact anniversary case remains insufficient evidence.
That deliberate uncertainty avoids inventing a service timestamp or inclusive cutoff that the short notice does not establish. The model is a review aid. Therefore, it is not a reproduction of GitHub’s internal scheduler, and it must not be used to predict the precise minute a repository changes state.
What the executed results establish
All eight results matched the expected outcomes retained in the input file. That confirms the small program follows our declared teaching rules for these inputs. It does not validate the platform’s implementation, measure alert coverage or estimate a national exposure rate.
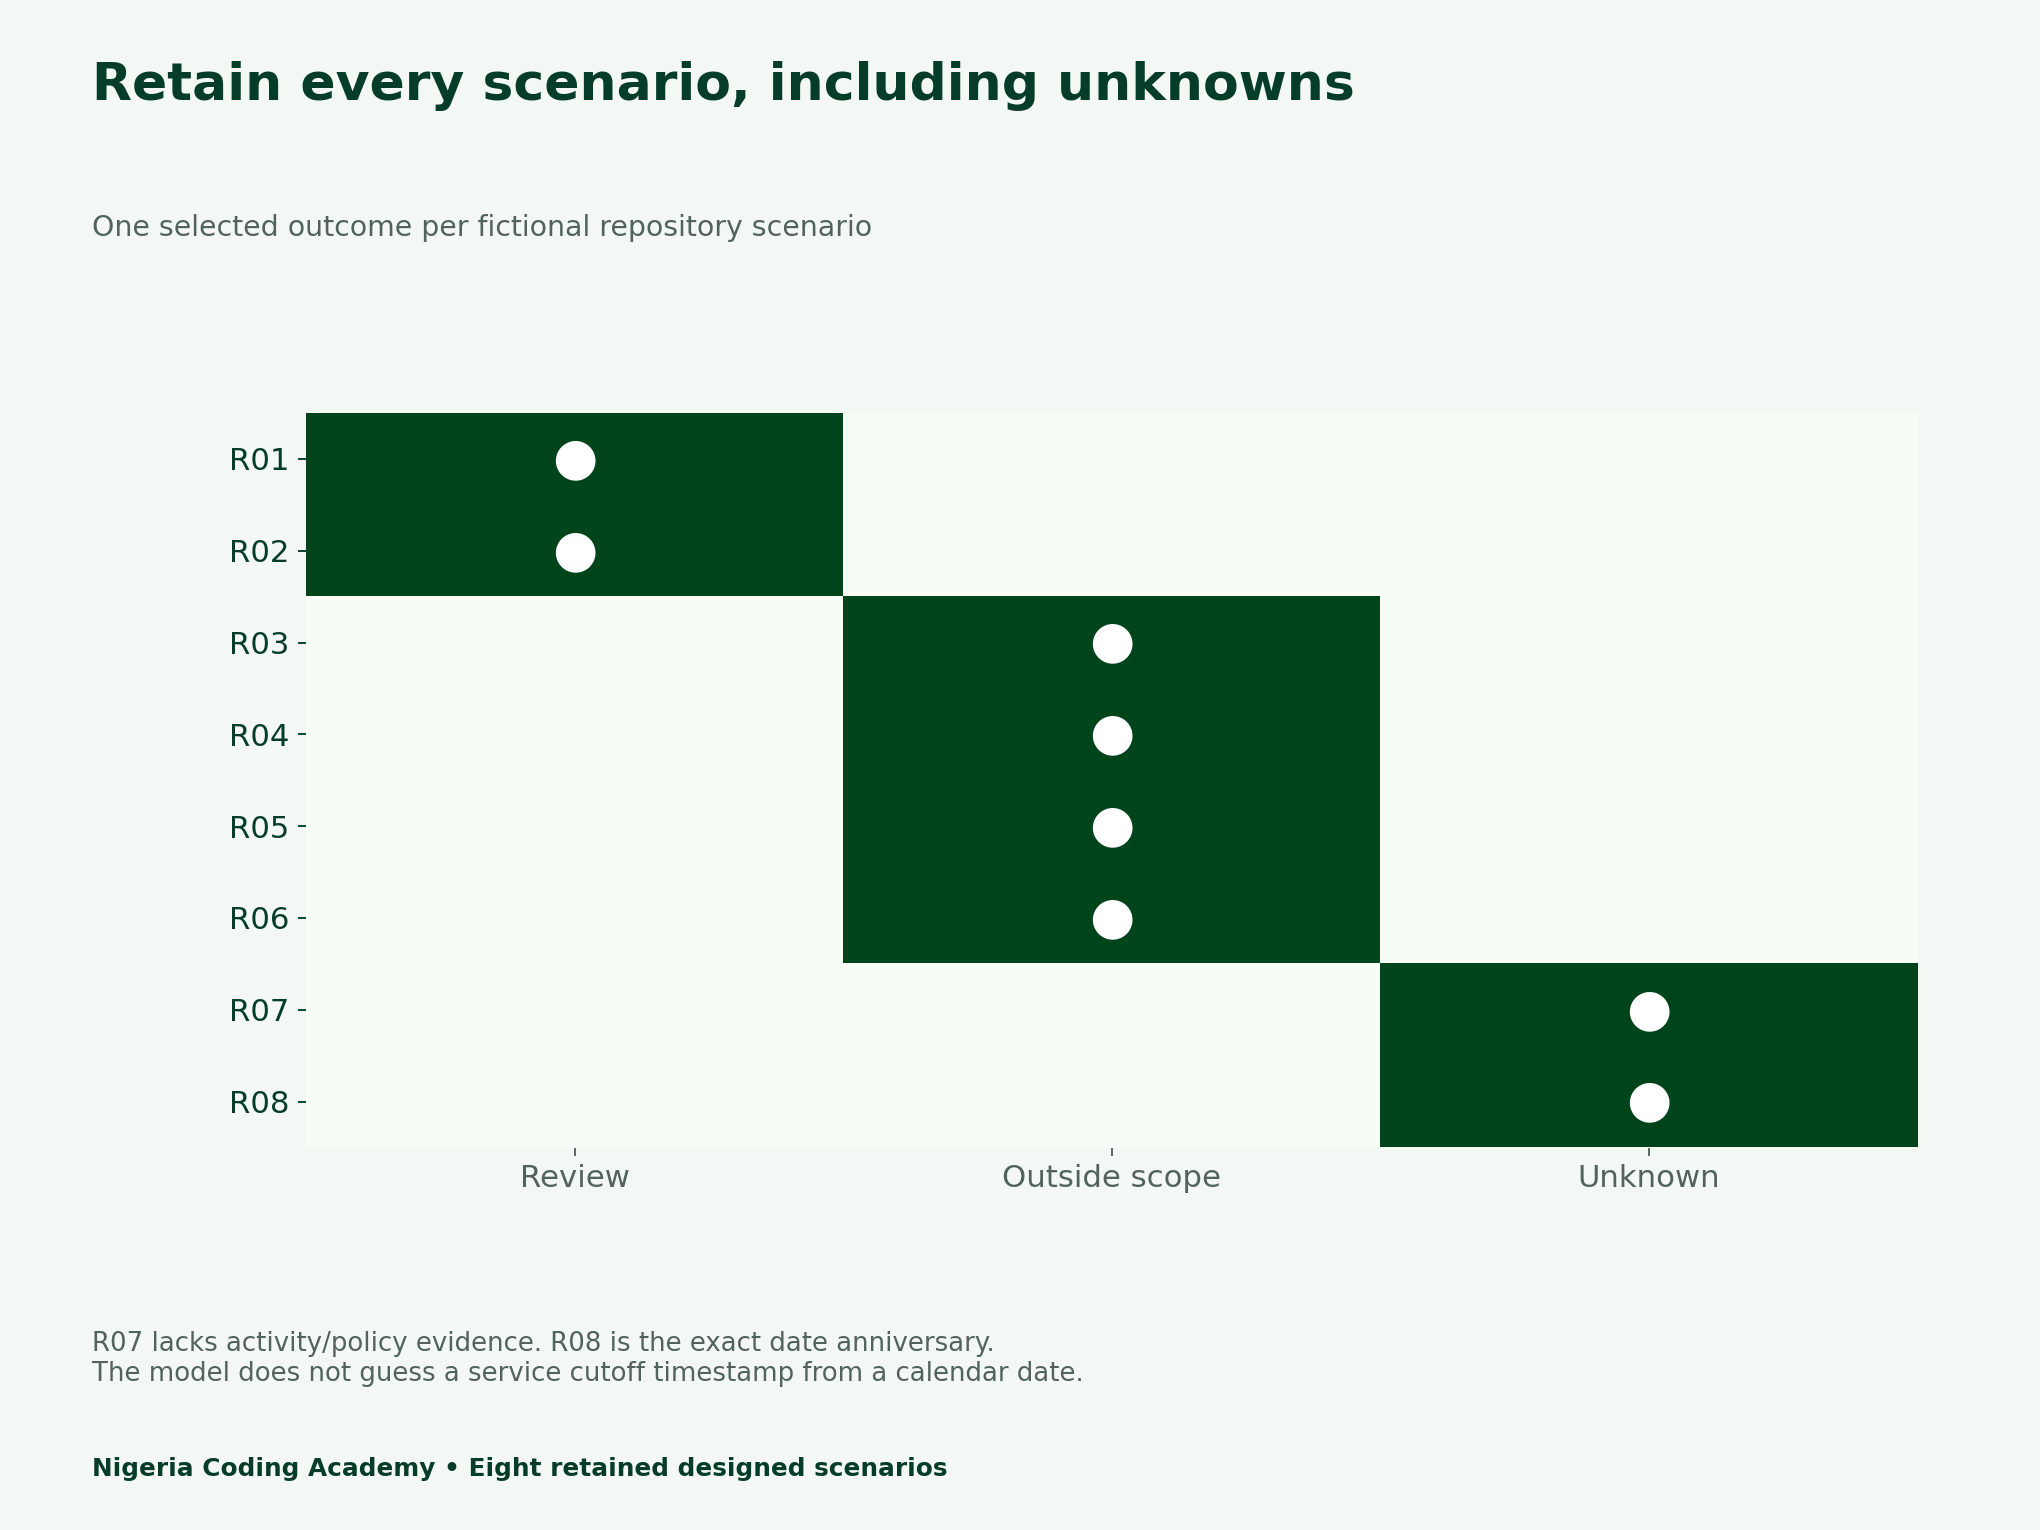
In addition, the downloadable ledger records a reason for each decision. For example, a known exception and recent activity can both lead outside this model’s inactivity scope, yet they do so for different reasons. Retaining the reason prevents a later reviewer from confusing policy evidence with evidence of recent development.
Inventory an older project without changing it
Start with the owner, purpose and whether the project remains deployed. Do not infer deployment from commit age. For example, a quiet demonstration can still be online, while an active repository can be an experiment that serves nobody. Record the evidence for that distinction.
Next, record the last qualifying activity you can substantiate, the current alert-enable state and any applicable policy exception. Note what dependency information exists and what remains unsupported or unknown. Use the blank inventory to keep a dated review trail rather than relying on memory.
For the current platform workflow, consult GitHub’s Dependabot alerts documentation. If a project remains in use, review authorised maintenance options and the current notice before changing settings. This article neither performs those changes nor recommends meaningless pushes to reset a clock.
Unlock Your Unique Tech Path
Get expert tech consulting tailored just for you. Receive personalized advice and solutions within 1-3 business days.
Get StartedWrite a claim that the evidence can support
A careful note might say that monitoring was checked on a stated date, identify dependency coverage and list unresolved findings. Avoid a blanket guarantee. If you cannot inspect the settings, record that limit and identify the person who can provide the missing evidence.
Similarly, do not publish private repository details in a portfolio worksheet. Our templates contain no credentials or customer records. They are designed for a learner to retain appropriate evidence privately and publish only a suitable summary.
Download the read-only review exercise
- Eight fictional monitoring-review scenarios (CSV)
- Expected and observed review outcomes (CSV)
- Blank repository monitoring inventory (CSV)
- Blank claim and supporting-evidence worksheet (CSV)
- Python review model, scenarios and instructions (ZIP)
For another status boundary, see our CI file-coverage study. Our issue-triage exercise shows why an unknown requirement deserves an explicit clarification outcome.
Methodology and limitations
We ran the standard-library model locally on 15 November 2026 using eight deliberately designed scenarios. We retain the source, expected labels, observed ledger and environment details. We accessed or changed no repository, policy, alert, dependency or credential.
The model is intentionally incomplete and date-based. Its counts are not a representative sample. It does not discover vulnerabilities or establish production suitability. Recheck official guidance before the announced enforcement date; the reusable result is the evidence discipline, not a forecast of an individual account’s state.


